@ZO-xQW358 has explained the behavior in a very good way. The OnGuard agent only send the posture status to ClearPass as a weblogin, and you should have a specific Service configure for this. This service only need to do return Dynamic Authorization (CoA) for all types of requests. Actually, if it was possible to create an enforcement policy without rules and only the default profile, that would have been enough. But you have to create at least one rule in an enforcement policy.
Just to add some extra information on the last step.
You have to remember to enable this checkbox in the Enforcement tab of your service:
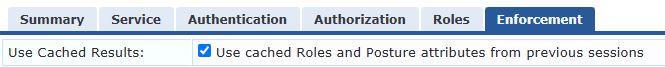
Otherwise the posture status will be lost and the client stuck in a loop.
During the second authentication you return a VLAN enforcement profile configured with the VLAN name or number for your quarantine VLAN.
Now you have Cisco switches, thus your Network Devices defined under Configuration \ Network \ Devices must have the Vendor set to Cisco, otherwise the Dynamic authorization (CoA) may not work. If you have created subnets and have both Cisco switches and Aruba AP's in the same subnet the Vendor setting will conflict for one or the other device type. The solution is to set the vendor field to the vendor with the largest amount of devices within a subnet and add the other vendors devices as IP addresses.
Let's say you have a /24 network with 100 access points and 10 switches.
Add the network as 10.11.12.0/24 and set Vendor to Aruba. Add the 10 switch IP addresses and set the Vendor to Cisco.
This way ClearPass will send the correct type of Dynamic Authorization (CoA) to both types of devices
------------------------------
Best Regards
Jonas Hammarbäck
MVP Guru, ACEX, ACDX #1600, ACCX #1335, ACX-Network Security
Aranya AB
If you find my answer useful, consider giving kudos and/or mark as solution
------------------------------
Original Message:
Sent: May 28, 2025 05:48 AM
From: zouhsaine
Subject: Aruba Clearpass 6.11 - Quarantine Vlan
As to my understanding, the agent is not the one that forces the Vlan, it just sends your posture status as (Healthy, Quarantine..) to Clearpass server, then the Clearpass server sends a CoA request (Bounce port, reauthenticate session ...) to the switch or AP, which forces a new authentication ,and this time Clearpass knows the posture status of the device, so Clearpass based on your policy rules will send a command to the switch/AP to put the device on the Quarantine VLAN in your case.
If you already configured the webauth service, all you need to do now is to add the Healthy/Non Healthy status in your dot1x rules
i recommend watching these videos:
https://www.youtube.com/playlist?list=PLsYGHuNuBZcb0xD05v9zdwv7NlUG_8oJS
search OnGuard videos on the list, there are 3 videos on this serie that explain it well.