Hi,
Just to be clear, there are three types of Custom Scripts that you can deploy using OnGuard.
- Health Collection,
- Auto Remediation
- Agent Enforcement Enforcement Profile.
Based on the information that you provided above I assume that you are going to be doing a Agent Enforcement Enforcement Profile, right?
Technically you can achieve that.
Here is a sample .ps1 script that will help you achieve that, but note that you will have to make adjustments.
# SimpleMapDrive.ps1
$share = "\\fileserver\shared"
$drive = "Z:"

# Wait a few seconds to ensure network access after COA
Start-Sleep -Seconds 10

# Try to map the drive
try {
    New-PSDrive -Name $drive.TrimEnd(':') -PSProvider FileSystem -Root $share -Persist -ErrorAction Stop
    Write-Host "Drive $drive mapped to $share successfully."
}
catch {
    Write-Host "Failed to map drive. Please check network access or credentials."
}
When you have the script on the Endpoint, please also make sure that these attributes are filled in correctly.
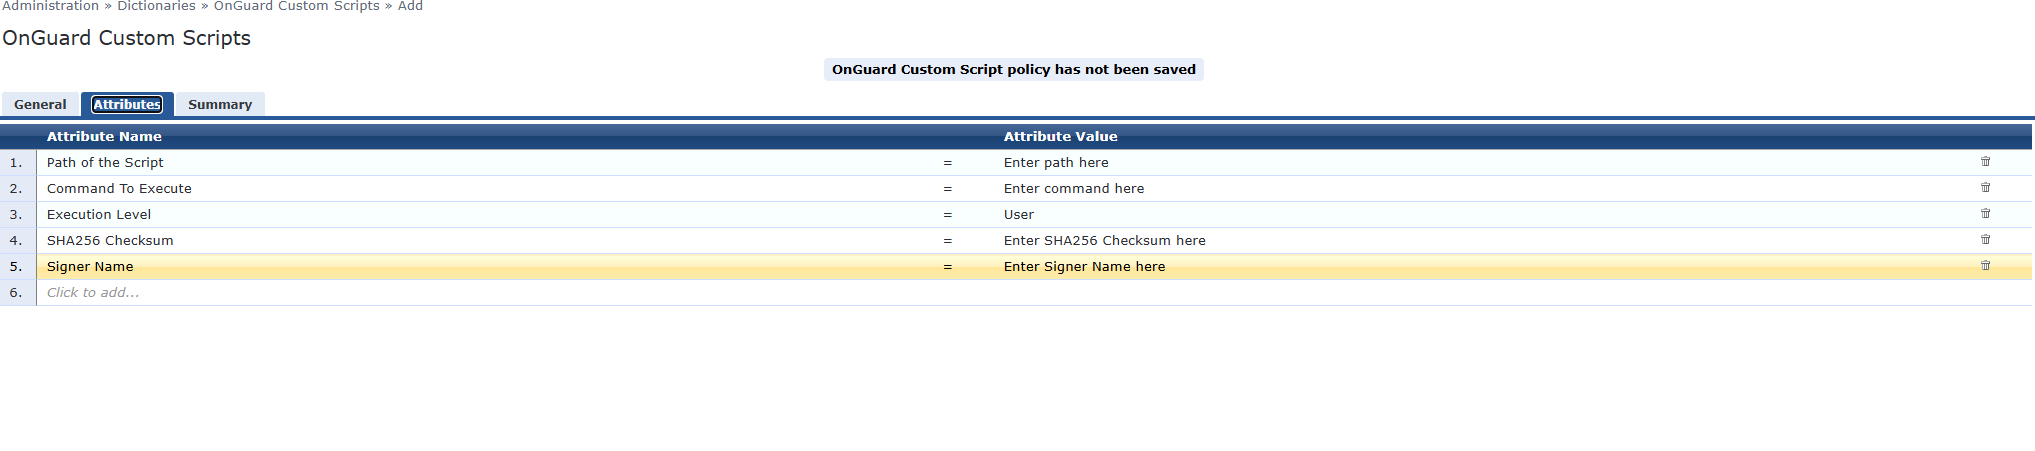
Lastly, you have to make sure that you have a local admin, or a admin user in any case that will be able to execute this script on the Endpoint., which is located under Administration>External Accounts, click on Add and it should be a Domain/WMI user.
One thing left to do afterwards is to push this enforcement profile on the service that you are using and troubleshoot any issues from there.
Hopefully this will answer your question.
Cheers,
Vigan
-------------------------------------------