Hello,
since we recently had a problem with one of the colleguaes bringing their own fritzbox for "i needed better wifi", we wanted to roll out DHCP Snooping across our Switches.
we have a few older switches that dont support DHCP Snooping, but most of them do and down below are the lines i configured for all of them:
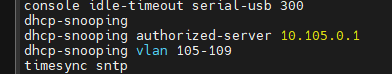
10.105.0.1 is that location's Domain Controller, DHCP, NTP Server and a few other things, our gateway is done by the firewall and sits on the 10.105.0.254, connected to the same Switch.
the VLANs on the location range from 80-110, but 105-109 are the only ones with an active DHCP and 106-109 the only ones important for clients. 105 is the Management VLAN that the Server and all our Switches are in, has a DHCP set up for the IPs of the Access points, Switches are static. we do not use Option 82 anywhere.
Our core is a flexfabric and thus was a bit differently configutred, not via authoriszed DHCP server IP, but with "trusted" Ports. since the Server isnt on the FF directly but one of the nearby switches, I set those switch uplinks as "trusted" ports.
from what i read, this should've been a simple config change that simply blocks out everything that ISNT the 10.105.0.1, but a few hour later, our first-level Support colleagues get multiple calls of their internet not working anymore, and all of those we checked getting an APIPA Address.
any idea where i went wrong with three lines of config?
-------------------------------------------