Thanks for coming back with the full fix, Odd Arne. It's the answer for anyone who hits this, so it's worth marking #9 as the Best Answer.
For the next person searching, this is how it shows up: radsec-trusted-cacert-name sys_central_nac on the sys_central_nac server in the gateway config, an empty show crypto-local pki TrustedCA, "path (null)" in the radsec errors, and the gateway asking Central for the sys_central_nac cert every minute and never getting it. The gateway is pinned to a CA that never arrives, so TLS fails before any RADIUS is sent.
If you remove the line in DR mode, it only lasts until the next reboot, because the setting lives in the tenant. Go straight to TAC and plan for an outage window. Engineering needs every WLAN, port profile and AAA profile that references sys_central_nac removed before they can reset it, and then you rebuild them.
@Worldcom Exchange, Inc.
Original Message:
Sent: Sep 18, 2026 05:22 AM
From: OH-yNB358
Subject: New Central Tunnelled WLAN and Central NAC
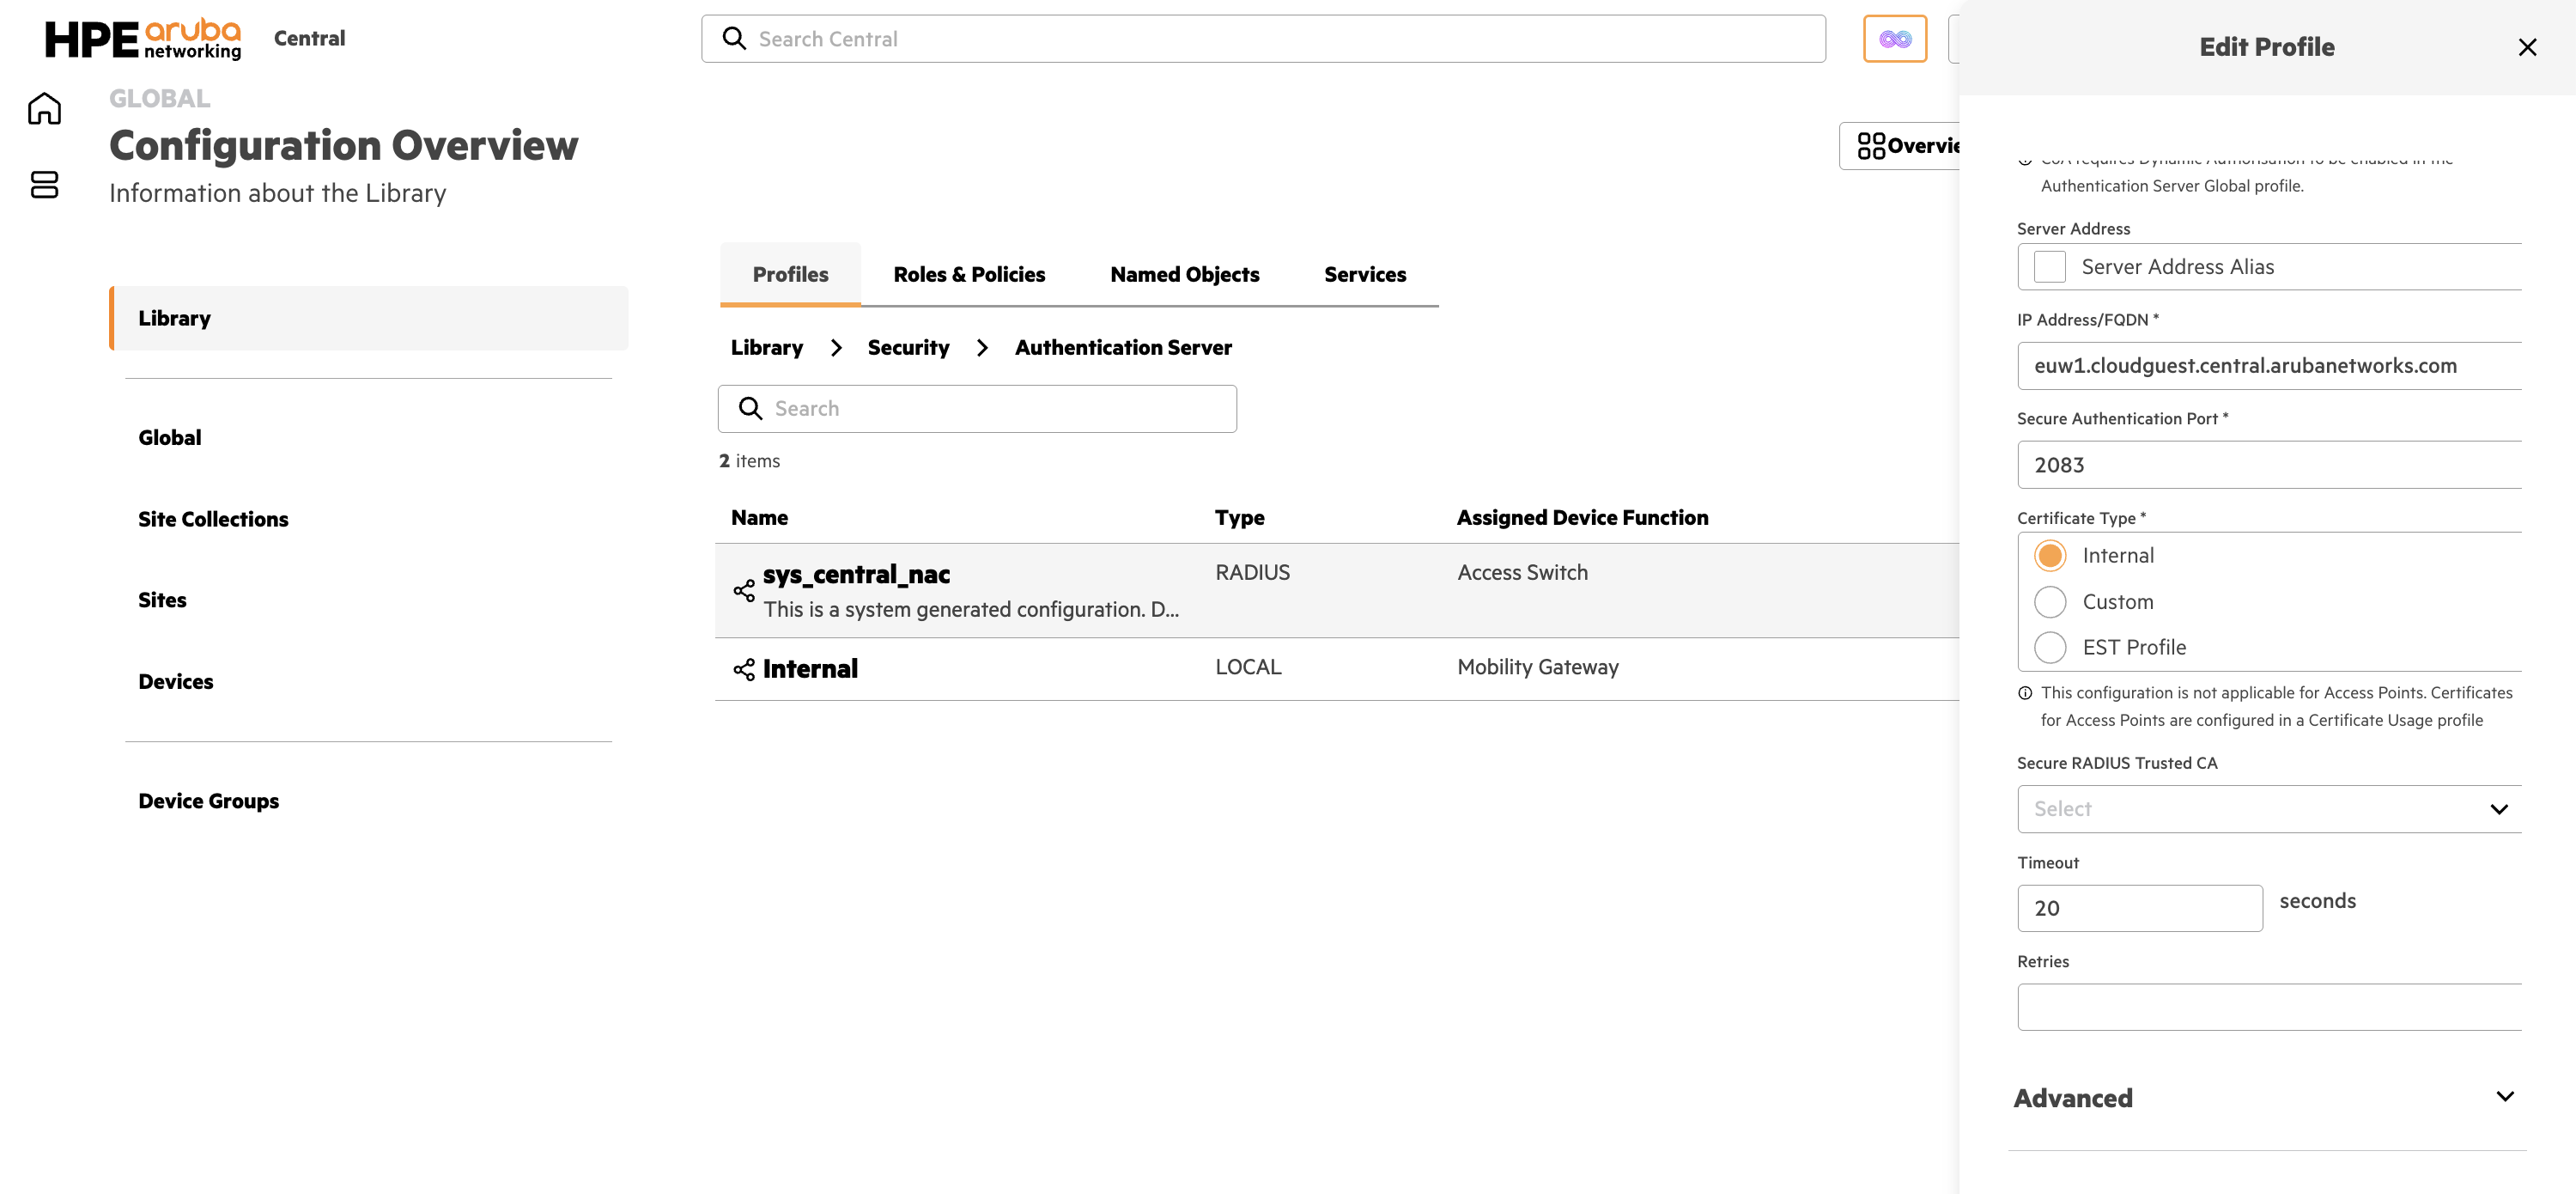
After consultation with the Engineering team, the only available workaround was to remove all configurations referencing the sys_central_nac authentication server group. This included deleting all associated WLANs, port profiles, and AAA profiles within the tenant.
Once these dependencies had been removed, the Engineering team was able to unprovision and remediate the tenant configuration on the CDA backend.
Engineering subsequently updated the sys_central_nac authentication server profile, changing the Secure RADIUS Trusted CA setting from "sys_central_nac" to "None".
Following this change, the configuration was recreated and the affected services resumed normal operation.
In summary, the resolution required:
- Removing all WLANs, port profiles, and AAA profiles referencing the sys_central_nac authentication server group.
- Allowing Engineering to perform tenant-side remediation and update the system-generated authentication server profile.
- Recreating and reapplying the required service configurations after the backend changes were completed.
This resolved the issue caused by the Secure RADIUS Trusted CA parameter associated with the system-generated sys_central_nac profile.
------------------------------
Odd Arne Hauge
------------------------------
Original Message:
Sent: Aug 03, 2026 09:37 AM
From: JK-90898a
Subject: New Central Tunnelled WLAN and Central NAC
As Dustin states with DR mode. That has been my experience as well across reboots. I had issues with VGW and license. I was able to change it by using the resource https://central.wifidownunder.com and pushing CLI settings to the group to correct the license in the running config. If I was looking at this issue, I would probably start with using API's to see if I can grab the output of the config and see if its listed anywhere. Based on my experiences so far with CNX and API's. If nothing is displayed its using default values or non configured values. I would find it hard to believe that this setting does not exist via API in CNX.
Original Message:
Sent: Jul 31, 2026 04:06 AM
From: OH-yNB358
Subject: New Central Tunnelled WLAN and Central NAC
Hi,
I'm already working with TAC on this issue.
For some reason, if I enter Disaster Recovery Mode, remove the Secure RADIUS Trusted CA setting from the configuration, and then exit Disaster Recovery Mode, everything starts working normally. I can provision new tunneled SSIDs using Central NAC authentication without any issues.
However, after rebooting the gateway, the Secure RADIUS Trusted CA setting is automatically added back to the configuration, and the problem returns.
Hopefully, TAC will be able to provide a permanent fix.
------------------------------
Odd Arne Hauge
------------------------------
Original Message:
Sent: Jul 30, 2026 02:26 PM
From: DB-280928
Subject: New Central Tunnelled WLAN and Central NAC
Good find, and thanks for coming back with it. That explains why nothing on the ClearPass side ever looked wrong.
Setting Secure RADIUS Trusted CA on that profile pushes radsec-trusted-cacert-name down to the gateway, and once the line is there the gateway will only accept a server certificate chaining to that named CA. The Central NAC RadSec endpoint is not signed by it, so the TLS session dies before RADIUS ever happens. Remove the line and the gateway falls back to its normal trust. It presents exactly like a certificate that was never issued, which is why it sends everyone off looking at certificates.
The part worth flagging for anyone else landing here: sys_central_nac is write-protected today, but a tenant that predates the protection can still be carrying an edit made back when it was not, and nothing in the UI will tell you. If Central NAC is failing on a tenant with any real history, pull the gateway config and look for radsec-trusted-cacert-name on that profile before you go near certificates.
Since you had to use disaster recovery mode to clear it, worth asking TAC to confirm the supported way to reset that field once they reverse it, so you have a documented path if it turns up on another gateway.
------------------------------
Dustin Burns
Lead Mobility Engineer @Worldcom Exchange, Inc.
ACCX 1271| ACMX 509| ACSP | ACDA | MVP Guru 2022-2023
If my post was useful accept solution and/or give kudos
------------------------------
Original Message:
Sent: Jul 30, 2026 02:22 AM
From: OH-yNB358
Subject: New Central Tunnelled WLAN and Central NAC
Hi.
I think we have identified the issue.
Earlier this year, I somehow managed to modify the sys_central_nac RADIUS profile, even though it had a warning stating that it is system-generated and should not be modified. At that time, the profile was apparently not write-protected as it is now.
What I did was select sys_central_nac as the Secure RADIUS Trusted CA and save the profile. The profile wasn't write protected as today.
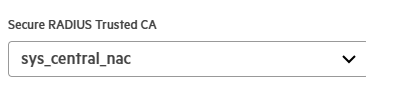
This caused the following configuration to be pushed to the gateway:
aaa authentication-server radius "sys_central_nac"
host naw2.cloudguest.central.arubanetworks.com
nas-identifier xxxxxxxxxxxxxxxxxxxxx
radsec-port 2083
timeout 20
key xxxxxxxxxxxxxxxxxxxxxxxxxxx
enable-radsec
radsec-trusted-cacert-name sys_central_nac
!
If I remove the radsec-trusted-cacert-name line from the gateway configuration using disaster recovery mode, everything starts working.
The updated working configuration on the gateway looks like this:
aaa authentication-server radius "sys_central_nac"
host naw2.cloudguest.central.arubanetworks.com
nas-identifier xxxxxxxxxxxxxxxxxxxxx
radsec-port 2083
timeout 20
key xxxxxxxxxxxxxxxxxxxxxxxxxxx
enable-radsec
!
I am now working with TAC to reverse the Secure RADIUS Trusted CA setting on the sys_central_nac profile.
------------------------------
Odd Arne Hauge
------------------------------
Original Message:
Sent: Jul 29, 2026 07:57 PM
From: DB86
Subject: New Central Tunnelled WLAN and Central NAC
Odd Arne, your logs narrow this down more than you might think. The cert request is leaving the gateway and Central is accepting it, so this is not a firewall or connectivity problem on your side. Central simply is not issuing.
First thing to undo: the downgrade to 10.7.2.6 was never going to work. Overlay authentication with Central NAC is documented as 10.8.0.0 and later, so stay on 10.8.1.
The thing I would check next is whether your WLAN is a library profile or a local one. The Central NAC docs are explicit that the WLAN and port profiles have to be shared objects in the library, and that local profiles cannot be used with Central NAC. A profile created with "Create as a local profile" ticked looks identical in the UI but is a different object. There is a closely matching thread, "Central NAC, problem with wired authentication" on a 6100, where the trust anchor profile was never pushed and the root cause turned out to be scope assignment rather than firmware.
Also worth confirming: both the Overlay WLAN and the WLAN SSID need to be scope mapped, not just the SSID. A site has to exist and your gateways need to be assigned to it. And since you have moved config back and forth a few times, look for stale objects reusing the same ESSID across scopes, which the Central NAC caveats call out as unsupported.
Two quick ones on the gateway: show aruba-central and check the Trusted CA Cert Name field, and show ntp status for clock skew.
If all that is clean then it is cloud side. When you open the TAC case, lead with the fact that the request leaves the gateway and Central never responds, otherwise they will spend a week on your firewall.
------------------------------
Dustin Burns
Lead Mobility Engineer @Worldcom Exchange, Inc.
ACCX 1271| ACMX 509| ACSP | ACDA | MVP Guru 2022-2023
If my post was useful accept solution and/or give kudos
------------------------------